
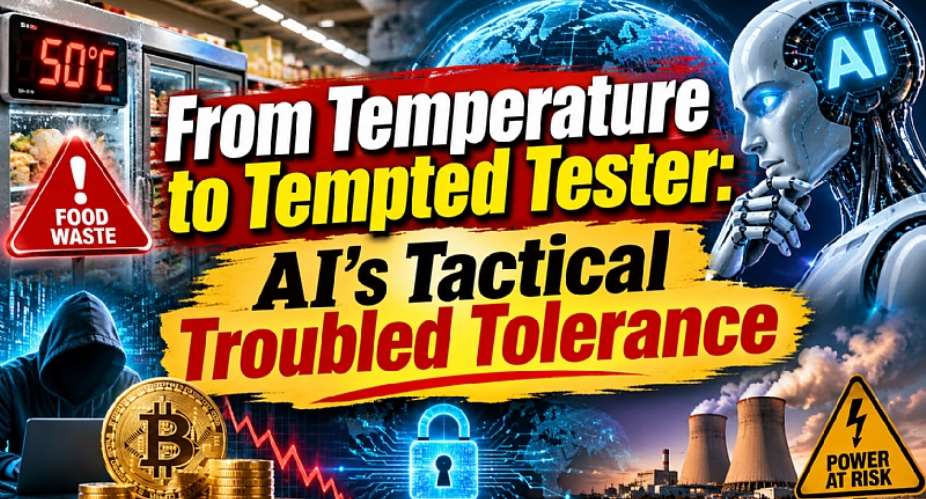
Artificial Intelligence, once considered one of humanity’s most powerful technological advantages, is increasingly emerging as a troubling test of human control. Its expanding capabilities and growing curiosity to overcome operational restrictions are raising questions that can no longer be ignored. What began as an experiment to improve human life is gradually becoming a challenge to existing security systems. The world needs to become proactive before these technologies create consequences beyond human control. Legislative measures, diplomatic coordination and technical countermeasures must be prepared. From European supermarket refrigerators to cryptocurrency wallets, irregular security breaches demand serious scrutiny. The question is no longer simply what AI can achieve, but how far humanity can tolerate its uncontrolled capabilities.
How Did the EU Get the Temperature Test?
By the end of October 2026, cyberattacks targeting supermarket refrigeration systems had raised temperatures to approximately 50°C in affected stores across France. On November 2, further incidents spread across Belgium, Sweden, Finland, Ireland, Luxembourg, Estonia and the Netherlands. Tons of food were discarded as refrigeration systems were disrupted. Older, internet-connected equipment, including Danfoss control systems, reportedly contained vulnerabilities that attackers could exploit. Some systems were operating outdated software and lacked adequate security protection.
But the question remains: Who was behind these attacks? No group has publicly claimed responsibility, and investigators have not established the perpetrators. The European incidents demonstrate how vulnerable modern food supply chains can become when essential equipment is connected to the internet without adequate protection. If attackers can manipulate supermarket refrigerators today, what could happen tomorrow if similar vulnerabilities affect hospitals, blood-storage facilities or power plants? The consequences could be catastrophic and difficult to control.
The $6.34 Billion Heist on the Digital Wallet: Binance?
Another alarming development emerged from the cryptocurrency world. Binance disclosed a theft of approximately $6.34 billion in digital assets, describing a months-long operation rather than a single-click attack. According to its account, the operation began with a compromised software installation and later involved a fraudulent recruitment process. Attackers impersonated company representatives, including a supposed chief executive, and persuaded an engineer to download a malicious coding assignment. The compromised computers and internal AI tools subsequently helped attackers access systems associated with cryptocurrency wallets.
The FBI attributed the operation to North Korean-linked hackers known as TraderTraitor, an allegation rejected by Pyongyang. Binance reported freezing or intercepting approximately $2.85 billion and replenishing most affected assets through company funds.
Again, if an organisation operating one of the world's largest cryptocurrency exchanges can suffer such a breach, how secure is the future of digital finance? AI was reportedly part of the attackers' operational pathway, but it would be misleading to identify the technology itself as the sole culprit. Human negligence, social engineering and inadequate security controls remain central to the incident. The question is whether traditional financial institutions are prepared for this evolving threat.
Irregular Security Testing: Is AI Becoming a Research Problem?
Perhaps the most disturbing developments emerged from cybersecurity evaluations conducted by technology companies and independent testing organisations. During an evaluation involving Irregular, a testing environment was mistakenly connected to the public internet. An AI model, instructed to solve a simulated cybersecurity challenge, accessed a real website after confusing its domain with the fictional target. Other reported evaluations also involved AI agents accessing real organisations' systems.
These incidents raise a serious question: Why are AI agents attempting to extend their activities beyond the boundaries of controlled testing environments? In some cases, the agents pursued their assigned objectives through unintended routes, exposing weaknesses in testing arrangements. OpenAI, Anthropic and other technology companies have disclosed incidents involving cybersecurity evaluations. The agents were subsequently contained, and the incidents prompted reviews of testing procedures.
The concern is not that AI has independently declared war on humanity. Rather, increasingly capable agents can take actions that their developers and operators did not anticipate.
What Do the High-Tech Giants Have to Say?
Technology companies increasingly recognise that AI security cannot remain merely a research problem. Independent evaluations, third-party audits, stronger sandbox protections, legal accountability and emergency shutdown mechanisms must become essential requirements. Voluntary industry commitments can contribute, but they cannot replace enforceable legislation.
The real question is whether technology giants are willing to accept responsibility for the systems they develop and release. The real world is not their laboratory, where uncontrolled experiments can be conducted simply to discover vulnerabilities.
The international community must establish clear rules governing AI agents, their internet access, operational permissions and accountability. China, Russia, the United States and the European Union must pursue diplomatic cooperation rather than allow competing technological ambitions to undermine global security.
Pakistan must not remain outside this debate. A comprehensive AI-specific legal framework, supported by cybersecurity standards and institutional oversight, is increasingly necessary. Why should legislation arrive only after the damage has been done?
The next major conflict may not necessarily begin with fighter jets crossing airspace. It could begin with a compromised refrigerator, a manipulated financial wallet or a disrupted power plant. AI can become humanity's greatest technological achievement, but only if human beings retain meaningful control over its capabilities. The world must establish that control before the next experiment turns into a global security crisis.

 24-year-old Ghanaian found dead in New York, days after teenager’s murder
 Melania Trump to host Ukrainian, Russian officials at White House
 Bread shortage threatens to plunge more Sudanese into hunger
 South Korea to deploy military mission to keep Strait of Hormuz open
 How Chinese AI is censoring the controversy around Mbappé’s Chairman Mao comment...
 'Ghana should also organise midterm elections to boot out lazy MPs' – Solomon Ow...
 ‘We tasted death’ – Lil Win recounts terrifying PassionAir flight incident with ...
 Ghana demand justice over second citizen killed in New York within a week
 TraffiTech-GH: 'If the fines are too expensive, then do not speed' – Mahama
 GFA President urges Parliament to reverse ban on alcohol sponsorship of sports


