
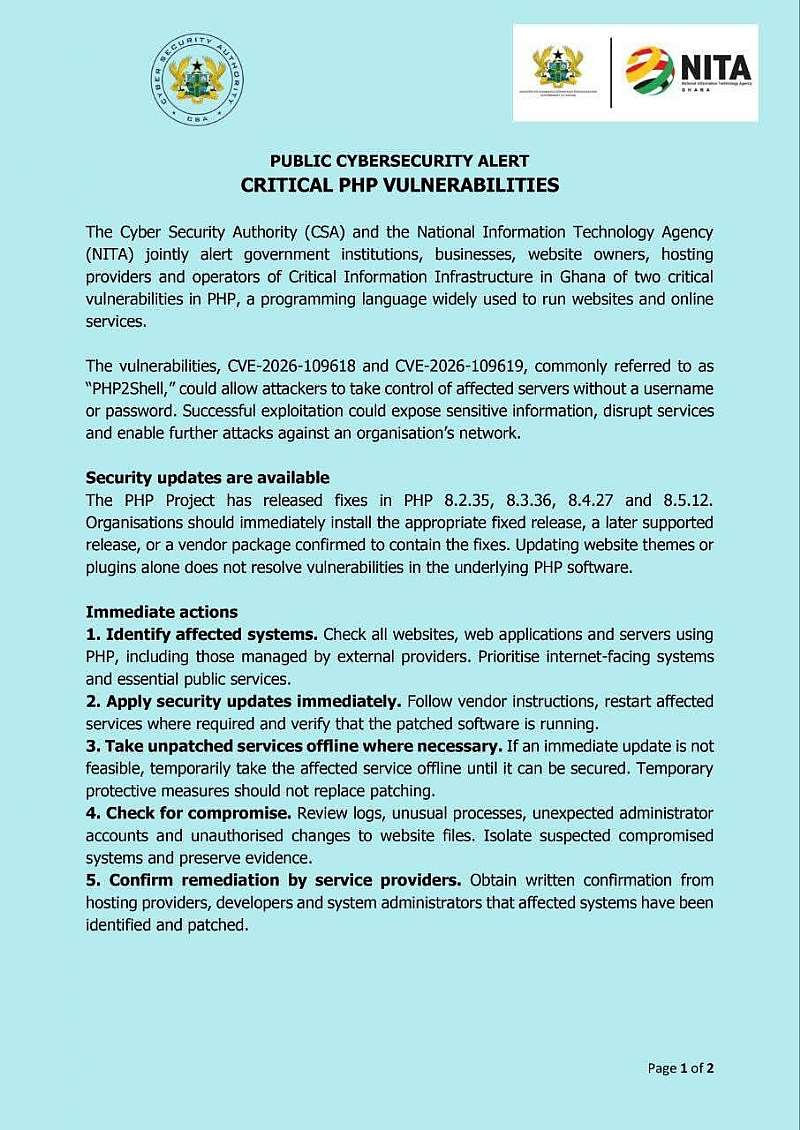
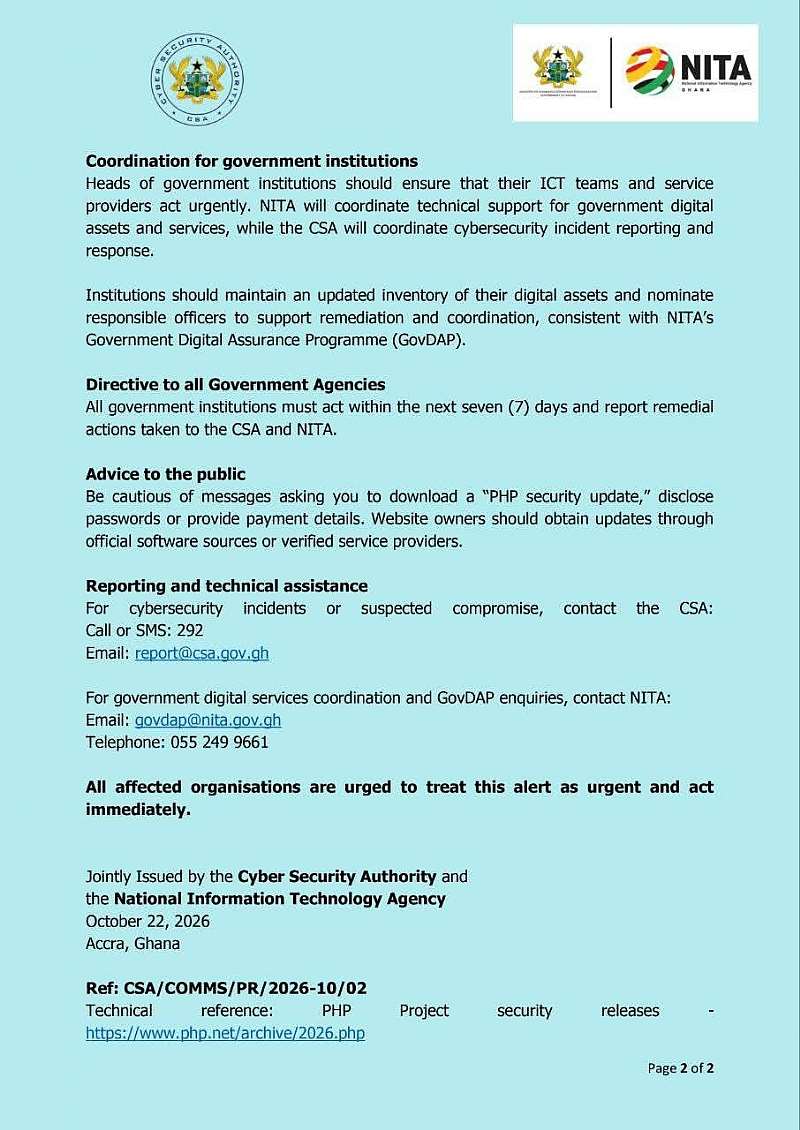
The Cyber Security Authority (CSA) and the National Information Technology Agency (NITA) have directed all government institutions in Ghana to address critical vulnerabilities in PHP software and report remedial actions within seven days.
The agencies cautioned that the vulnerabilities could allow attackers to take control of affected servers without requiring usernames or passwords, potentially exposing sensitive information and disrupting online services.
In a joint cybersecurity alert issued on Thursday, October 22, the agencies urged government institutions, businesses, website owners and hosting providers to install security updates immediately.
“The vulnerabilities, CVE-2026-109618 and CVE-2026-109619, commonly referred to as ‘PHP2Shell,’ could allow attackers to take control of affected servers without a username or password,” the statement said.
The agencies said the PHP Project had released security fixes in versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12, urging affected organisations to install the appropriate fixed or later supported releases.
They cautioned that updating website themes or plugins alone would not resolve vulnerabilities in the underlying PHP software.
The CSA and NITA also directed organisations to identify affected systems, prioritise internet-facing websites and essential public services, and check for signs of compromise, including unusual processes, unauthorised administrator accounts and changes to website files.
Organisations unable to apply the updates immediately have been advised to temporarily take affected services offline where necessary until they can be secured.
Under the directive, heads of government institutions are expected to ensure that their information and communications technology teams and service providers act urgently and report the measures taken to both agencies within seven days.
“NITA will coordinate technical support for government digital assets and services, while the CSA will coordinate cybersecurity incident reporting and response,” the statement added.
The agencies said institutions should also maintain updated inventories of their digital assets and designate officers to support remediation efforts under NITA’s Government Digital Assurance Programme.

 New Economy policy must address Ghana’s skills gap and import dependence – Sam O...
 GES mourns four pupils killed in Aboabo Junction accident
 CSA, NITA issue seven-day directive to government agencies to patch critical PHP...
 Critics unfairly expect Prof Opoku-Agyemang to make emotional statements about i...
 Obuasi SHTS sexual abuse: Let's not get overly emotional to hang an innocent man...
 Africa faces 'complex' Ebola outbreak after spread to Nigeria: WHO
 Kwame Dzokoto reportedly dead
 Ghana intensifies airport screening and Ebola surveillance amid reported cases i...
 15,000 aspirants to contest NDC constituency executive elections this weekend
 October 22: Cedi sells at GHS12.25 on forex market, GHS11.66 on BoG interbank


